What attackers do to sign-in pages
• Code bombing: request hundreds of sign-in codes for one victim's email.
• Code guessing: try codes from many IPs, a few each.
• Throwaway signups: create accounts with disposable emails to abuse free tiers.
• Slow and spread out: a few attempts per IP per minute stays under most rate limits.
Why a generic limit isn't enough
• Cloudflare Free: 5 custom rules and one rate-limiting rule that counts per IP over 10 seconds.
• It can't count per email, or per hour, or wrong codes only.
• It needs your DNS on Cloudflare.
• Sign-in needs rules that understand sign-in.
The rules
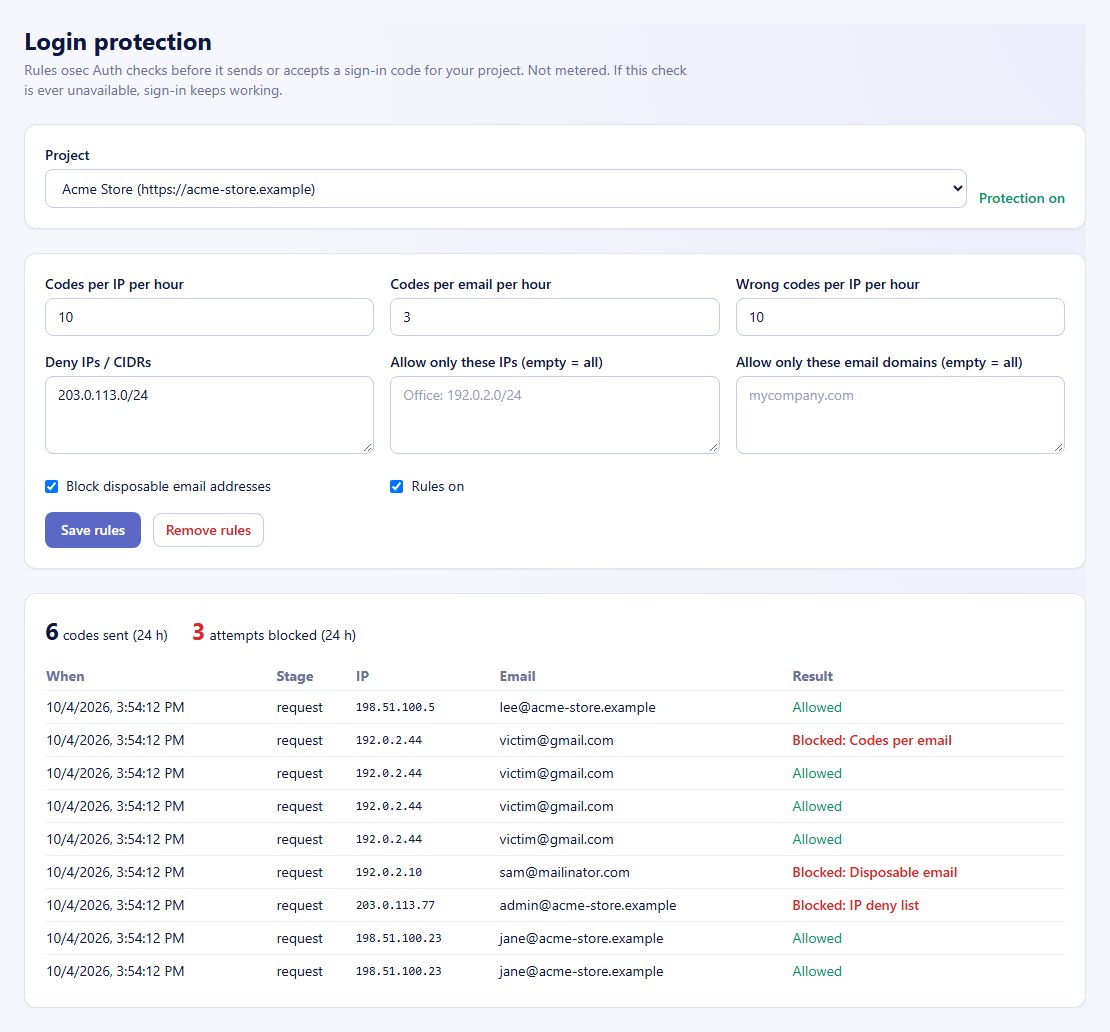
• Codes per IP per hour (default 20).
• Codes per email per hour (default 5): stops code bombing even across many IPs.
• Wrong codes per IP per hour (default 20): stops guessing.
• IP deny list and IP allow list (CIDR), e.g. office-only admin apps.
• Allowed email domains: only @yourcompany.com can sign in.
• Block disposable emails: 9,000+ throwaway domains.
Turn it on
1. Sign in at osec.one → Console → Login protection.
2. Pick your osec Auth project.
3. Adjust the limits, add IP or domain lists, tick Block disposable emails.
4. Save. Rules apply within 30 seconds.
5. Watch the log: allowed codes and blocked attempts for the last 24 hours.
What your users see
• A clear message in the sign-in dialog, e.g. "Too many sign-in codes requested. Try again in an hour."
• Office-only rules: "Sign-in isn't allowed from this network."
• Domain rules: "Use your organization's email address to sign in."
Good to know
• Not metered: rule checks don't count against your daily quota.
• Fails open: if the rule check is ever unavailable, sign-in works as before.
• Email code, Google and Apple: IP lists, allowed domains and disposable-email blocking apply to all three; code limits apply to email codes.
• No passwords to protect: osec Auth is passwordless, so there's nothing to spray or stuff in the first place.
Passwordless sign-in plus rules that understand sign-in. Free.
Protect your sign-inSources
• Cloudflare WAF custom rules, plan availability: https://developers.cloudflare.com/waf/custom-rules/
• Cloudflare rate limiting rules, plan availability: https://developers.cloudflare.com/waf/rate-limiting-rules/
• OWASP, credential stuffing prevention: https://cheatsheetseries.owasp.org/cheatsheets/Credential_Stuffing_Prevention_Cheat_Sheet.html
• Disposable email domain list (open source): https://github.com/disposable-email-domains/disposable-email-domains