Where we started
• Grade F, 5 out of 100, on our own scanner. Embarrassing for a security brand.
• Missing: Strict-Transport-Security, Content-Security-Policy, X-Content-Type-Options, Referrer-Policy, Permissions-Policy, clickjacking protection.
• Leaking: Server: nginx/1.24.0 (Ubuntu) on every response.
• Fine already: HTTP to HTTPS redirect, TLS 1.0/1.1 off, no mixed content.
What we changed
1. One file, /etc/nginx/snippets/osec-security-headers.conf, with six add_header … always; lines.
2. include it in the server block, and again in every location that sets its own add_header (nginx drops inherited headers there).
3. server_tokens off; in a conf.d file.
4. nginx -t, then reload. No restart, no downtime.
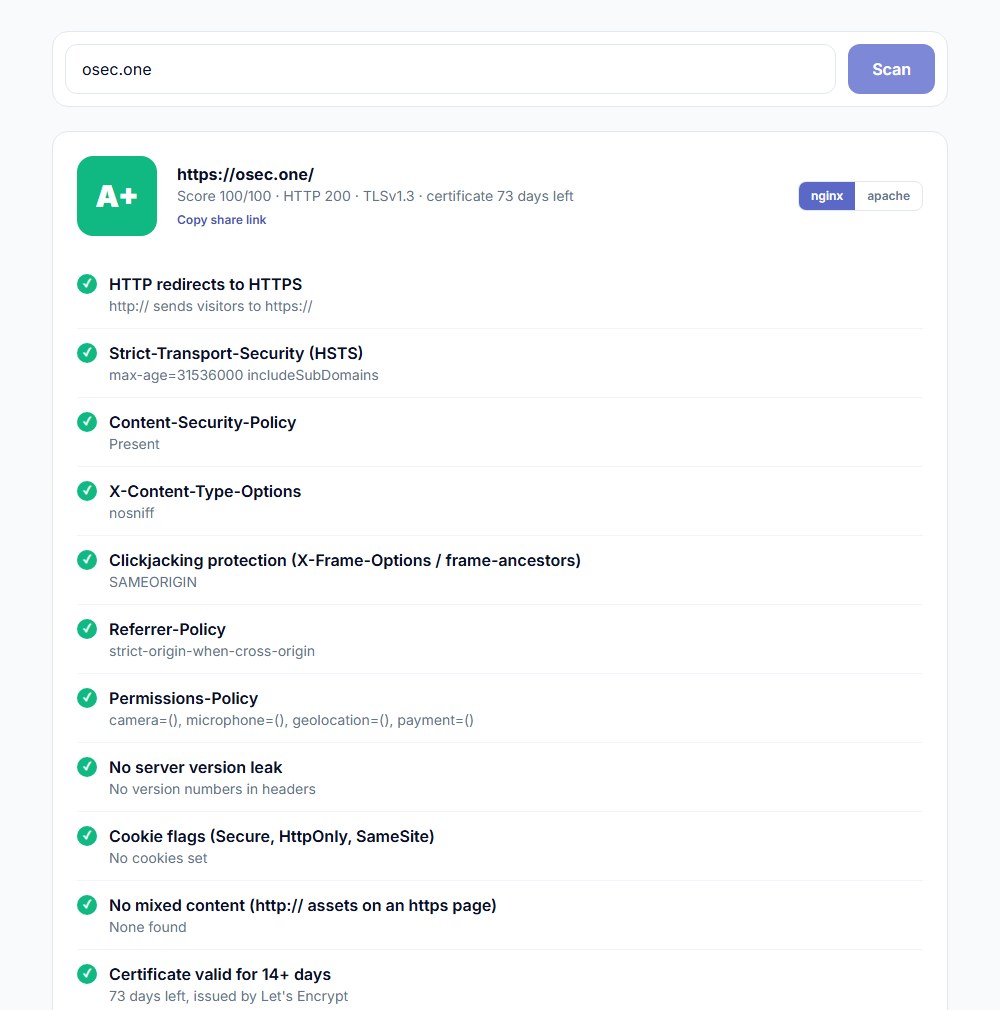
5. Rescan: A+, 100 out of 100.
The six headers, in plain words
• Strict-Transport-Security: browsers only ever use HTTPS for your site.
• Content-Security-Policy: limits where scripts, frames and plugins can come from. Start small: frame-ancestors 'self'; object-src 'none'; base-uri 'self'.
• X-Frame-Options: nobody can frame your pages to trick clicks.
• X-Content-Type-Options: nosniff: files are only run as what they claim to be.
• Referrer-Policy: full URLs don't leak to other sites.
• Permissions-Policy: no camera, microphone or location unless you need them.
Grade your site
1. Open osec.one/tools/scan.
2. Enter your domain.
3. Read the red items. Each has an nginx and an Apache fix.
4. Apply, reload, scan again.
5. Share the result link with your host or developer.
What it checks
• HTTPS redirect, HSTS, CSP (and weak values like 'unsafe-inline'), nosniff, clickjacking, Referrer-Policy, Permissions-Policy.
• Server and framework version leaks.
• Cookie flags: Secure, HttpOnly, SameSite.
• Mixed content, third-party scripts and missing integrity hashes.
• Certificate validity, TLS 1.3, old TLS 1.0/1.1, security.txt.
• Not a vulnerability scanner: it only looks at what any browser gets from your URL.
Good to know
• Free: 5 scans a day without an account; signed in, each scan is one request of your 500 a day.
• CSP breaks things if rushed: start with Content-Security-Policy-Report-Only and send reports to osec CSP Reports.
• Behind Cloudflare? Add the headers with a Transform Rule, or at your origin.
Free security header and TLS grade with copy-paste fixes.
Scan your siteSources
• MDN, HTTP security headers: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers
• OWASP Secure Headers Project: https://owasp.org/www-project-secure-headers/
• nginx add_header inheritance: https://nginx.org/en/docs/http/ngx_http_headers_module.html#add_header