In April 2025 one of the UK's best-known retailers lost its online shop for 46 days. Marks & Spencer's chairman told Parliament that the attackers got in on 17 April 2025 through a "sophisticated impersonation" that involved a third party. The ransomware was DragonForce, and the people behind the intrusion are widely linked to Scattered Spider. M&S has not published a full technical report, so this analysis separates what M&S, Parliament, the National Crime Agency and its own results say from what was only reported.
What is established and what is not
| Claim | Status | Source |
|---|---|---|
| Entry on 17 April 2025 through impersonation involving a third party | Established | Chairman Archie Norman, Business and Trade Sub-Committee, 8 July 2025 |
| Attackers detected on 19 April, crisis team that night, public statement 22 April | Established | M&S evidence to Parliament, summarised by Triumcyber |
| Ransomware was DragonForce, with other "loosely aligned" actors | Stated by M&S chairman | Evidence of 8 July 2025, Infosecurity Magazine |
| The impersonation was a call to the outsourced IT help desk that reset a password or MFA | Reported, not confirmed by M&S | BBC and trade press; TCS says its systems were not the source |
| Attackers are Scattered Spider | Reported, widely believed | Four people aged 17 to 20 arrested by the NCA on 10 July 2025 over M&S, Co-op and Harrods; no charges announced in the sources used |
| Whether a ransom was paid | Not disclosed | Norman declined to say, citing law enforcement |
On the help-desk mechanism, to be plain: M&S said "impersonation" and "third party". The detail that an outsourced service desk reset credentials comes from press reporting, and Tata Consultancy Services, which ran M&S's service desk, has said its own systems and staff accounts were not breached. In late October 2025 the press reported that M&S had moved its service desk to another provider; M&S did not describe that as a finding about the attack.
Step 1: the impersonation (17 April)
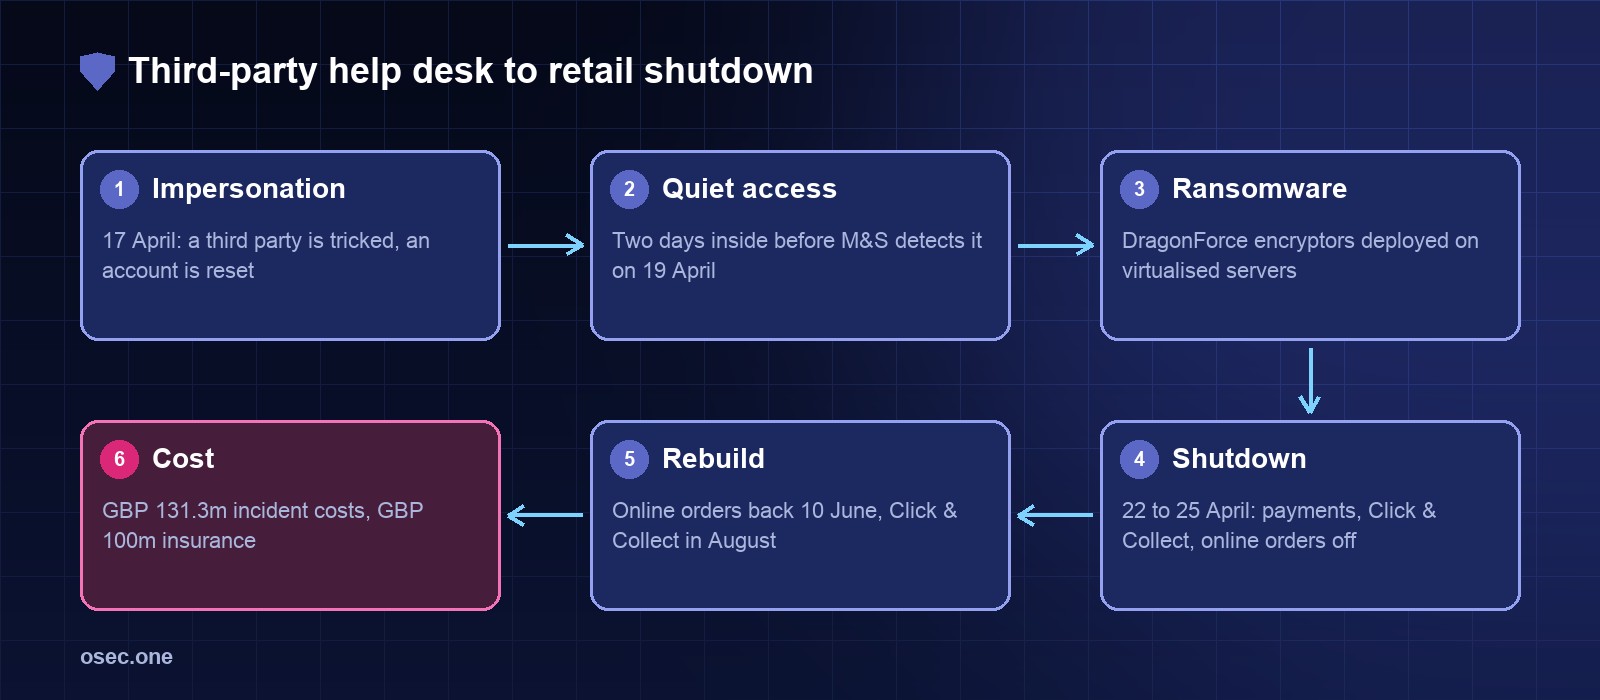
Scattered Spider's known method, set out in CISA's advisory AA23-320A and in our MGM and Caesars analysis, is to phone support, pose as an employee and ask for a password or MFA reset. The data they need (name, role, manager, employee number) is mostly public or bought. Against M&S the entry date, 17 April, was a Thursday before the Easter weekend, when staffing is thin and a rushed help-desk agent has the most reason to say yes.
The same pattern appeared at the contractor level in Okta and Lapsus$ 2022: the weak point was a support organisation with real reset powers over somebody else's accounts.
Step 2: two days of quiet access (17 to 19 April)
M&S detected the attackers on 19 April, two days after entry. In those two days a ransomware crew with a valid account does what the MGM crew did: find the identity system, escalate, find the virtualisation layer. M&S has not detailed this. Reported claims that the domain database was copied are not in M&S's evidence and are left out here.
Step 3: shutdown, as the visible damage (22 to 25 April)
| Date | Event |
|---|---|
| 17 April | Initial access through impersonation involving a third party |
| 19 April | Attackers detected; crisis team convened that night |
| 22 April | M&S discloses a cyber incident; contactless payments and Click & Collect disrupted in stores |
| 25 April | All online orders for clothing, home and beauty paused (UK, Ireland, international) |
| 10 June | UK online orders resume for some clothing lines: 46 days after the pause (Reuters) |
| 10 July | NCA arrests four people over the M&S, Co-op and Harrods attacks |
| August 2025 | Click & Collect restored, some services still down (The Register, 11 August) |
| 5 November 2025 | Half-year results: £101.6 million of incident costs booked in the first half |
| Year to 28 March 2026 | Full-year: £131.3 million incident costs, £100 million insurance |
Stores stayed open with manual workarounds, and food availability suffered because stock allocation was done by hand. M&S said its systems rebuild would take months and that it deliberately disconnected systems, including warehouse management, to contain the attack.
What it cost, in M&S's own numbers
| Item | Figure | Source |
|---|---|---|
| Estimate given in May 2025 | About £300 million lost operating profit before mitigation | M&S, May 2025 |
| Online outage cost | Roughly £10 million of profit per week (witness summary) | Parliament evidence |
| Incident costs, full year to 28 March 2026 | £131.3 million, of which £109.3 million systems response and recovery | M&S full-year results |
| Insurance proceeds | £100 million | M&S full-year results |
| Net incident cost after insurance | £31.3 million (our arithmetic: 131.3 - 100) | Derived |
| Half-year sales, fashion, home and beauty | -16.4%; UK online -42.9%; stores -3.4% | M&S half-year results, 5 Nov 2025 |
| Half-year food | Sales +7.8%, profit -58.8% from markdowns and waste during manual allocation | The Register, 5 Nov 2025 |
| Half-year adjusted profit before tax | -55.4% to £184.1 million; operating margin 12% to 2.7% | M&S half-year results |
| Full-year adjusted profit before tax | -23.8% to £671.4 million | M&S full-year results |
Two worked checks. The outage at £10 million a week for 46 days (6.6 weeks) is about £66 million of lost online profit, a fifth of the £300 million headline. And £671.4 million after a 23.8% fall implies roughly £881 million the year before (671.4 / 0.762), a drop of about £210 million. That drop includes more than the attack (the half-year report also shows a packaging levy of over £50 million), so it is an upper bound for the incident, not a measurement of it. The Cyber Monitoring Centre classed M&S and Co-op together as one event with estimated losses of £270 million to £440 million.
How Co-op got off lighter
The Co-op was breached about two weeks later, reportedly by the same actors. Reports say ransomware only succeeded at M&S because Co-op shut systems down before the encryptors could be deployed; Co-op witnesses told Parliament that heavily segmented systems limited the effect. M&S, by contrast, had a hybrid legacy and modern estate with about 50,000 people on its systems across employees, contractors and outsourced teams, which M&S itself said complicates mapping lateral movement and restoring in the right order.
Controls that break each step
| Step | Control | Check |
|---|---|---|
| Impersonation of staff on a help desk | Reset only after video check against HR photo, callback to a number on file, or manager approval. Same strength as the login it replaces | Out-of-band approval per reset, logged |
| Outsourced desk with broad reset powers | Give the contractor no ability to reset privileged accounts or MFA; privileged resets stay with an in-house team | Separate queue for admin and finance users |
| Valid account used for two days | Alert on a reset followed by a new MFA device or a sign-in from a new location within minutes; no admin rights from a fresh enrolment | Reset-then-enrol alert to the security team, not the help desk |
| Move to the hypervisors | Separate admin identities for virtualisation, phishing-resistant MFA, management network off the user network | Hypervisor logins from jump hosts only |
| Encryption and long outage | Offline tested backups, a rebuild order for core systems, segmentation so one domain compromise doesn't reach everything | Practise the "turn it off" decision as Co-op did |
| Manual fallback | Tested paper or offline processes for stock allocation and payments (M&S's food profit fell 58.8% in the half under manual allocation) | Rehearse the fallback with real volumes |
What to take from it
1. Account recovery is authentication. Scattered Spider has used the same help-desk route at MGM, Caesars and, on M&S's own account, an impersonation with a third party. A reset path that accepts LinkedIn facts is the weakest login you have.
2. Outsourcing the desk outsources your reset power. Decide exactly which accounts a contractor can touch, and keep admin resets in-house.
3. The cost is the outage, not the ransom. M&S's costs were recovery work and lost sales; a decision to switch off early, as Co-op reportedly did, is worth practising.
4. Insurance paid about 76% of the incident cost (100 / 131.3), but not the sales that did not happen.
A password a support agent can reset is a password an attacker can ask for. osec.one logins use one-time codes and Apple/Google sign-in, so your customers have no password to reset. Free to start.
Add passwordless loginSources: UK Parliament, Business and Trade Sub-Committee, M&S evidence session, 8 July 2025; Triumcyber summary of the session; Infosecurity Magazine: M&S chair details the attack; Reuters via StreetInsider: 46-day pause ends; The Register: M&S pegs cleanup costs, 5 Nov 2025; The Register: Click & Collect restored, 11 Aug 2025; ISMS.online: M&S results reconstruction (full-year figures); NCA: four arrested over M&S, Co-op and Harrods; CISA AA23-320A: Scattered Spider.